Introduction
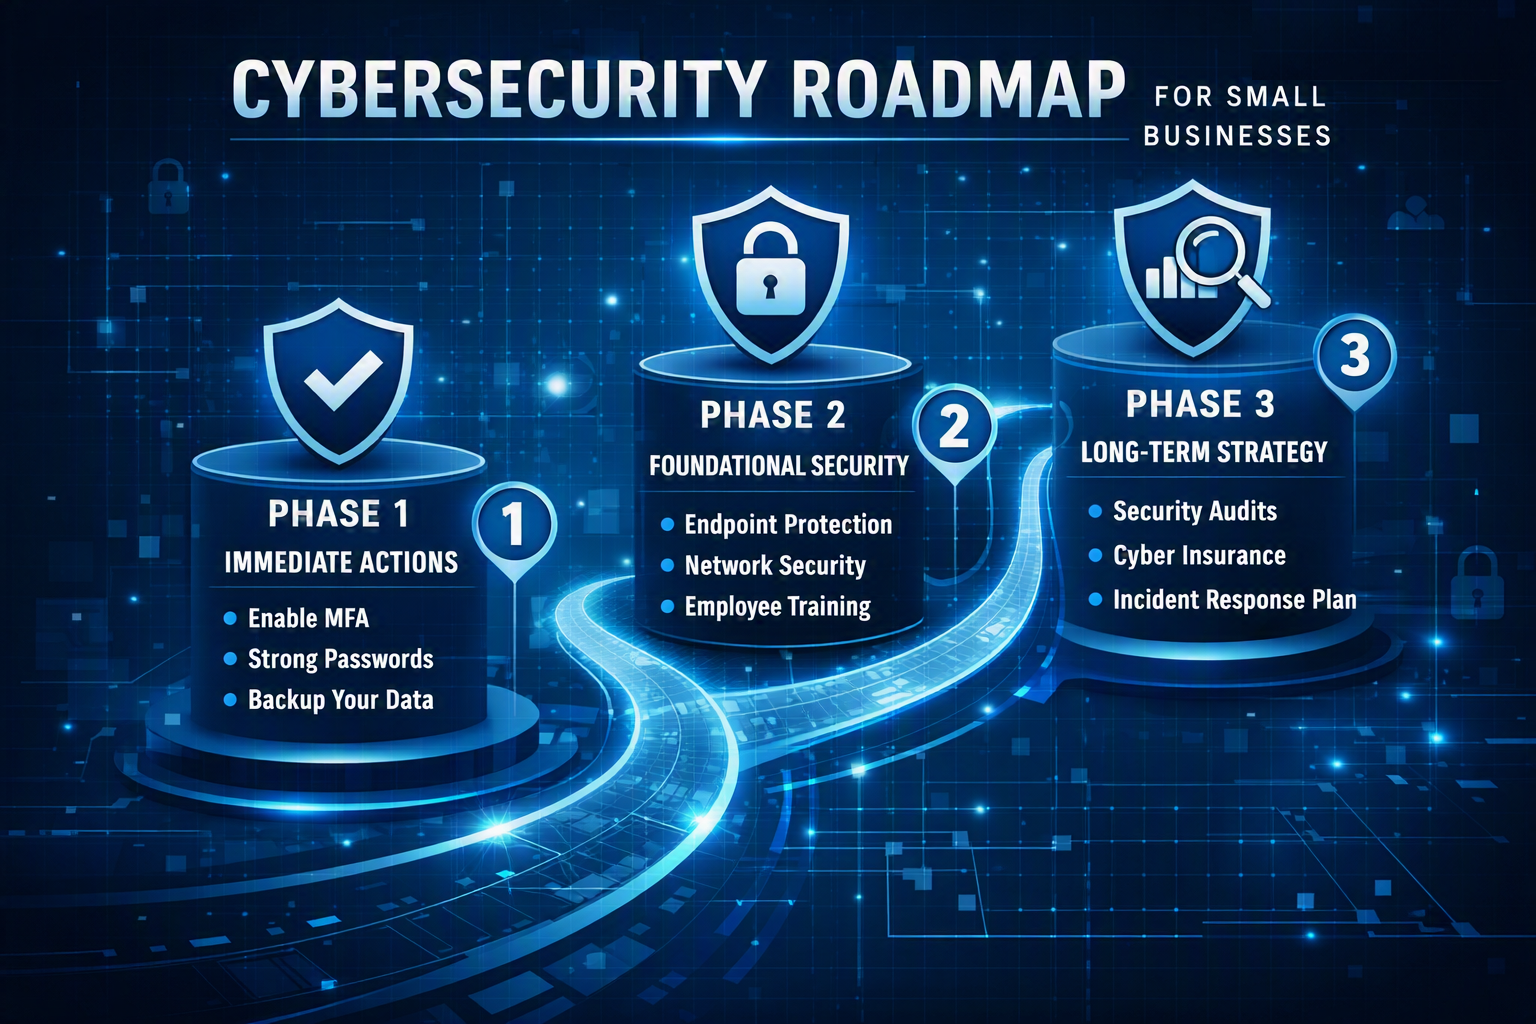
Most small businesses know they should improve cybersecurity, but they don’t know where to start or how to prioritize. This roadmap breaks the process into three clear phases—Immediate, Foundational, and Long‑Term—so you can strengthen your defenses without overwhelming your team or your budget.
Phase 1: Immediate Fixes (Today–Next 7 Days)
These are the “stop the bleeding” steps. They cost little, take minimal time, and eliminate the biggest risks.
1. Turn on Multi‑Factor Authentication (MFA) Everywhere
- Banking
- Cloud apps (Microsoft 365, Google Workspace, QuickBooks, CRM)
- Remote access tools
This alone blocks the majority of credential‑based attacks.
2. Enforce Strong Passwords
- Minimum 12 characters
- No reuse across accounts
- Use a password manager (Bitwarden, 1Password, Keeper)
3. Enable Automatic Updates
- Windows/macOS
- Browsers
- Mobile devices
- Key applications
Unpatched software is one of the most common breach points.
4. Set Up Automated Backups
- Daily cloud backups
- At least one offline backup
- Test restore once per quarter
Backups turn disasters into inconveniences.
5. Remove Old Users and Unused Apps
- Former employees
- Old contractors
- Abandoned SaaS tools
Every forgotten account is a potential attack path.
Phase 2: Foundational Improvements (Next 30–90 Days)
These steps build a stable, secure foundation.
6. Deploy Endpoint Protection
Modern antivirus + behavior monitoring Examples: Defender for Business, SentinelOne, CrowdStrike Falcon
7. Secure Your Network
- Replace outdated routers
- Disable default passwords
- Separate guest Wi‑Fi
- Block risky ports
8. Implement Basic Security Policies
- Acceptable use
- Password policy
- Device policy
- Remote work policy
Policies don’t need to be complicated—they just need to exist.
9. Train Employees on Cyber Hygiene
Short, monthly micro‑trainings on:
- Phishing
- Safe browsing
- Social engineering
- Handling sensitive data
People are your biggest risk—and your biggest defense.
10. Centralize Your IT Management
Use tools that let you:
- Push updates
- Enforce policies
- Monitor devices
- Track vulnerabilities
This is where small businesses start feeling “enterprise‑level” protection.
Phase 3: Long‑Term Strategy (Next 6–12 Months)
These steps mature your security posture and reduce long‑term risk.
11. Conduct an Annual Security Audit
Review:
- Access controls
- Software inventory
- Backup health
- Patch compliance
- Incident response readiness
Audits catch problems before attackers do.
12. Evaluate Cyber Insurance
Understand:
- What’s covered
- What’s excluded
- What security controls insurers require
- How premiums are calculated
Insurance is becoming a necessity, not a luxury.
13. Build an Incident Response Plan
Document:
- Who to call
- What systems to isolate
- How to communicate
- How to restore operations
A plan turns chaos into a checklist.
14. Consider Advanced Protections
As your business grows:
- SIEM monitoring
- Zero‑trust access
- Vulnerability scanning
- Penetration testing
These are optional but powerful.
Conclusion
Cybersecurity doesn’t have to be overwhelming. With a clear roadmap, small businesses can strengthen their defenses step by step—starting with simple fixes and building toward long‑term resilience. The key is consistency, not perfection.
Related Posts
 How Much Should a Business Spend on Cybersecurity? A Practical Budgeting Guide
 The 10 Most Common Cybersecurity Mistakes Small Businesses Make